Datadog BYOC adds cross-cluster queries for logs, for teams and AI agents
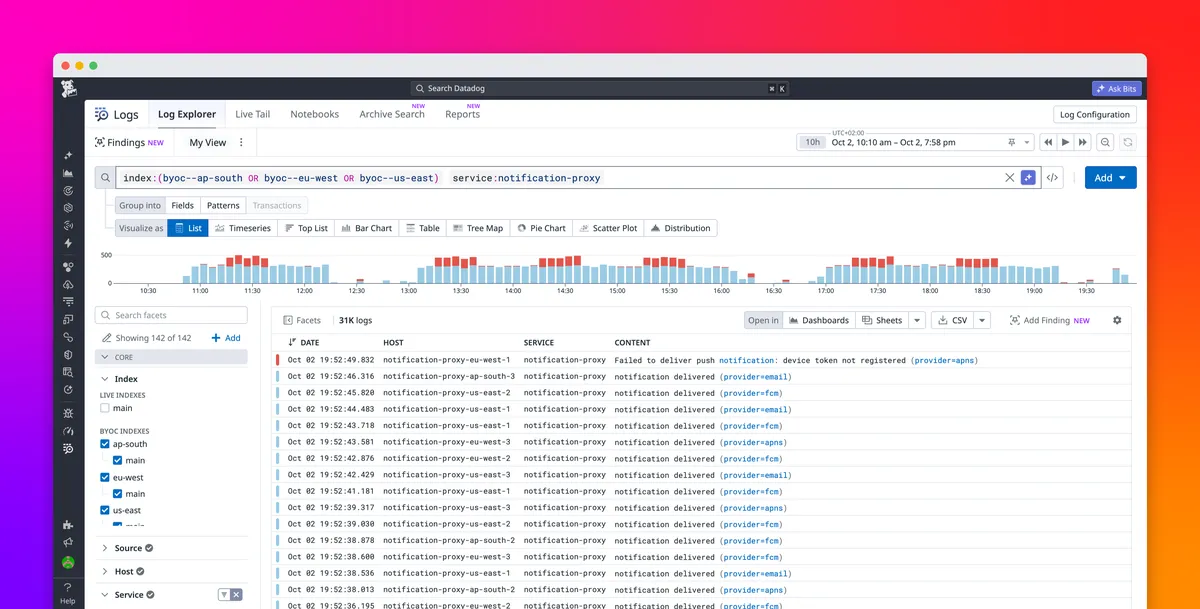
Datadog has introduced cross-cluster queries for its Bring Your Own Cloud (BYOC) Logs, letting teams and AI agents search selected BYOC clusters with a single query. The logs stay in their original locations, while Datadog runs the query on each cluster and combines the matches in the Log Explorer.
- Datadog BYOC Logs now supports cross-cluster queries that search selected clusters with one query.
- Logs remain in their original locations; Datadog combines matching results in the Log Explorer.
- AI agents can use the feature through the Datadog MCP Server and the search_datadog_logs tool.
- Datadog says it may reduce tokens spent on repeated tool calls, but total usage depends on returned results.
- The same query scope works in dashboards and log monitors; customers should contact their Datadog account team for access.
Why BYOC investigations were split up
Some organizations need to keep data in specific regions or on infrastructure they control, because of data residency requirements, internal policies or transfer costs. According to Datadog, its BYOC offering extends the platform into those environments. Each BYOC deployment runs as a Kubernetes cluster with its own object storage, which keeps data close to its source. Teams keep using Log Explorer, dashboards, monitors, Bits AI and the MCP Server, and can benefit from existing cloud pricing and discounts.
The downside, as Datadog describes it, is that deployment boundaries complicate investigations that span regions or business units. If an error shows up in Frankfurt, engineers may need to know whether Virginia or Mumbai is affected as well. Searching each cluster separately means repeating queries and filters and then comparing results by hand.
How cross-cluster queries work
In the Log Explorer, users define the scope of an investigation by selecting the BYOC indexes they want to search. They can pick the indexes in the facet panel or name the clusters directly with the index filter. Datadog returns matching logs in one list, and changes to filters or the time range apply across all selected clusters. From there, the usual Log Explorer workflow applies: open a single log, inspect its attributes and refine the next search.
To focus on one dataset, users can specify an index's qualified name, such as byoc--eu-west--application. This helps when a cluster holds several datasets but only one is relevant. The naming format is explained in the BYOC Logs search documentation.
Datadog gives two example queries:
- Tracking a suspicious IP address across business units: index:(byoc--finance OR byoc--commerce) @network.client.ip:203.0.113.42 service:login
- Checking whether a regional incident is global: index:(byoc--us-east OR byoc--eu-west OR byoc--ap-south) service:notification-proxy status:error
The second query helps tell an isolated deployment failure from errors that affect several regions. If the evidence points to one cluster, the query can be narrowed to it.
AI agents and ongoing monitoring
Datadog also targets AI-driven investigations. Through the Datadog MCP Server, agents can query BYOC logs with search_datadog_logs, specifying indexes, filters and a time range. With cross-cluster queries, an agent looking into notification failures can search the Virginia, Frankfurt and Mumbai deployments together instead of coordinating separate regional searches.
According to Datadog, consolidating those searches can reduce the tokens spent on repeated tool calls and on processing response metadata. The company adds a caveat: the agent still has to process the matching logs, so total token usage depends on the results returned and any follow-up requests.
The same scope can be used for continuous monitoring. Datadog describes a travel-booking platform running in Virginia, Frankfurt and Mumbai, where some payments are processed outside the region in which a booking originates. A dashboard could track booking and payment errors across all three regional clusters, and a log monitor could evaluate payment failures against one shared alert condition. When the monitor triggers, engineers can use the same cross-cluster search to look at the affected transactions.
What it means for BYOC customers
For organizations that chose BYOC to meet residency or cost requirements, the feature aims to remove the need to pick between keeping logs local and getting a combined view of an incident. Datadog says teams can investigate services across regions and business units without changing where their logs are stored.
Access is not self-serve in the source: Datadog tells customers to contact their account team to discuss access for their deployment. The company points to its cross-cluster search documentation for query syntax and index naming, and to the BYOC Logs documentation for deployment and configuration guidance.