Fake Claude Code extension sat in Cursor's marketplace for 11 hours
A tampered build of Anthropic's Claude Code extension, version 2.1.313, was available in Cursor's VS Code extension marketplace on October 29 and tried to install a persistent SSH backdoor, according to Kilo Code's account of the incident. Up to 5,000 users may have installed it.
- A tampered Claude Code extension, version 2.1.313, was live in Cursor's marketplace from about 2:27am to 1:35pm PT on October 29.
- Up to 5,000 users may have installed it, and it tried to plant a persistent SSH backdoor with an attacker key labeled svc-telemetry.
- Uninstalling is not enough: the payload leaves scripts running, so affected users should run Cursor's remediation script and rotate credentials from a clean machine.
- Kilo Code recommends allowlisting publishers, pinning versions, disabling unreviewed auto-updates and running editors without admin rights.
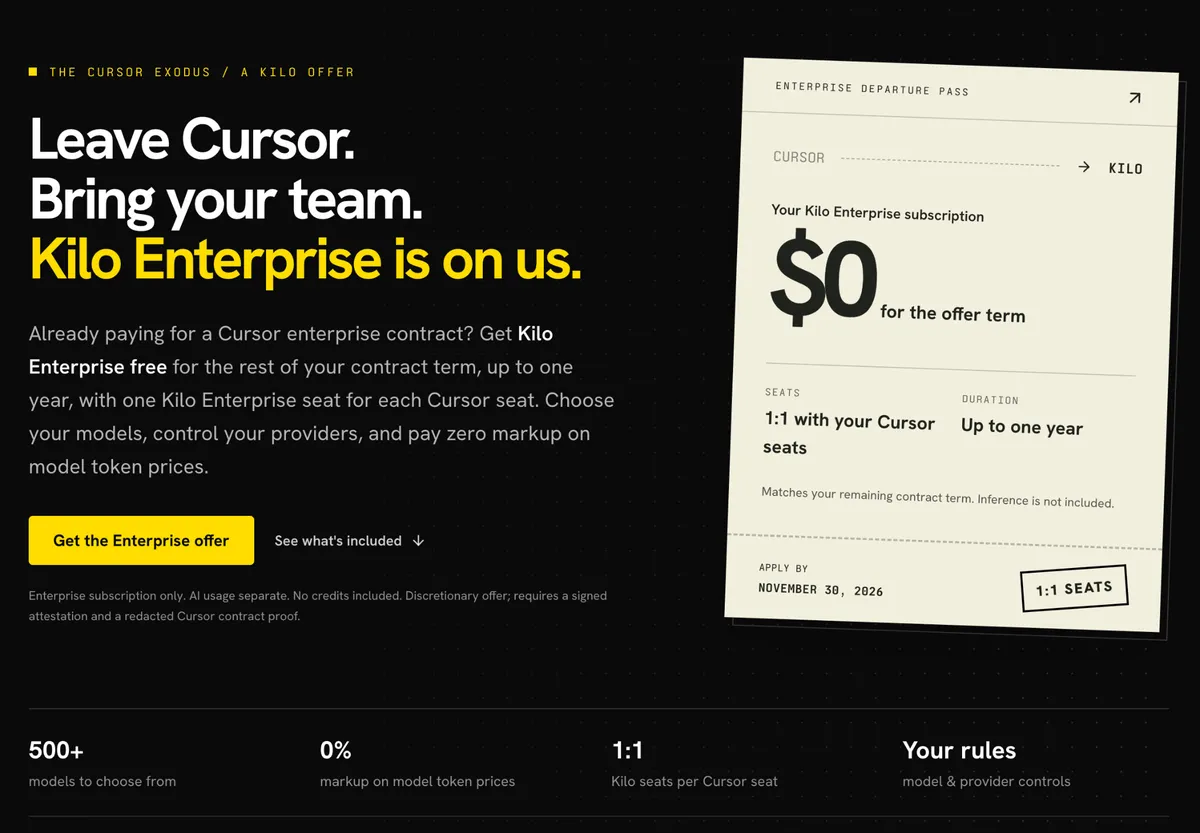
- Kilo offers Kilo Enterprise free for the rest of a Cursor contract, up to 12 months, with applications open until November 30, 2026.
What happened in Cursor's marketplace
Anthropic did not build the extension. According to Kilo Code, the malicious version was live from about 2:27am to 1:35pm PT on October 29. Cursor caught it, pulled it, shut down the marketplace, rotated keys and worked with the host to take the attacker's server offline. The company also published a detailed security notice, which Kilo Code says deserves credit.
Kilo Code argues the attack was simple: a trusted name, a new version number, and an install or auto-update. That was enough.
What the malicious build did
Based on Cursor's findings as relayed by Kilo Code, the extension tried to plant a persistent SSH backdoor. It did the following:
- Collected host details: hostname, username, OS, home directory, environment variable names, Git email and public IP.
- Added an attacker-controlled SSH key, labeled svc-telemetry, to authorized_keys.
- Tried to enable the local SSH service and open a reverse tunnel. This failed on most machines because it needs admin rights.
- Installed persistence through a LaunchAgent on macOS or a scheduled task on Windows, retrying the tunnel every 60 seconds.
- Reported back to the attacker over HTTP.
Anyone who installed or updated that version during the window should check for the svc-telemetry key, run Cursor's remediation script and rotate credentials from a clean machine. Uninstalling the extension is not enough, because the payload leaves scripts that keep running. Cursor's notice contains the full steps and indicators of compromise.
Know your AI toolchain
Kilo Code says AI coding tools now run a growing stack of add-ons: extensions, MCP servers, skills and plugins. Many can read a repository, run shell commands and touch the environment. In its words, the software supply chain has moved into the editor, and most teams are not watching it yet.
For each add-on, the post says teams should be able to answer four questions: who made it, what changed since the last trusted version, what it does, and what it is allowed to do. Its practical steps include:
- Allowlist publishers and pin versions for anything with shell or file access.
- Do not let agent extensions auto-update unreviewed.
- Run editors without admin rights. In this incident, missing admin rights stopped the worst step on most machines.
- Review MCP servers like dependencies.
- Watch persistence spots such as ~/.ssh/authorized_keys, LaunchAgents, scheduled tasks and startup folders.
- Centralize policy rather than leaving each developer to decide alone.
Kilo's pitch and the Cursor Exodus offer
Kilo Code concedes that no editor is immune and notes that Kilo also ships as an extension. It points to its open-source code on GitHub, Kilo Enterprise admin controls (model and provider settings per org, SSO, SCIM, role-based access and audit logs), provider policies and guardrails built with Enkrypt AI. Admins are due to get a single place to enable guardrails for all users, plus MCP Scan and Skill Scan by Enkrypt AI to check MCP servers and skills before they run.
The post also cites model access changes at Cursor. It says OpenAI has stated it will not supply future models to Cursor following Cursor's acquisition by SpaceX, with OpenAI model access in Cursor scheduled to end November 12, 2026. Cursor's new X Subscription plans, it adds, drop the included third-party model allowance.
Against that backdrop, Kilo is offering Kilo Enterprise free for the rest of a Cursor enterprise contract, up to 12 months, with seats matching Cursor seats 1:1. It lists 500+ models with zero markup on token prices through the Kilo Gateway, and support for bringing your own keys, local models or eligible ChatGPT Plus and Pro subscriptions. Applications close November 30, 2026. AI usage is billed separately with no credits included, the offer is discretionary, and it requires a signed attestation and a redacted proof of the Cursor contract. It does not cancel or reimburse the Cursor contract.
What it means for teams
The incident shows how little it took to reach developer machines through a trusted extension name. Kilo Code's advice is to audit the AI toolchain this week, whichever editor is in use, and to avoid depending on a single vendor's marketplace or provider deals. Teams weighing a switch can pilot Kilo on real repositories alongside Cursor, compare quality and cost, and then roll out, according to the post. Note that the guidance comes from a competitor of Cursor, which also promotes its own offer.
Kilo Code: Know Your AI Toolchain: Lessons from the Cursor Marketplace Incident