IST: US and China Need a Routine AI Incident Line Before a Crisis Hits
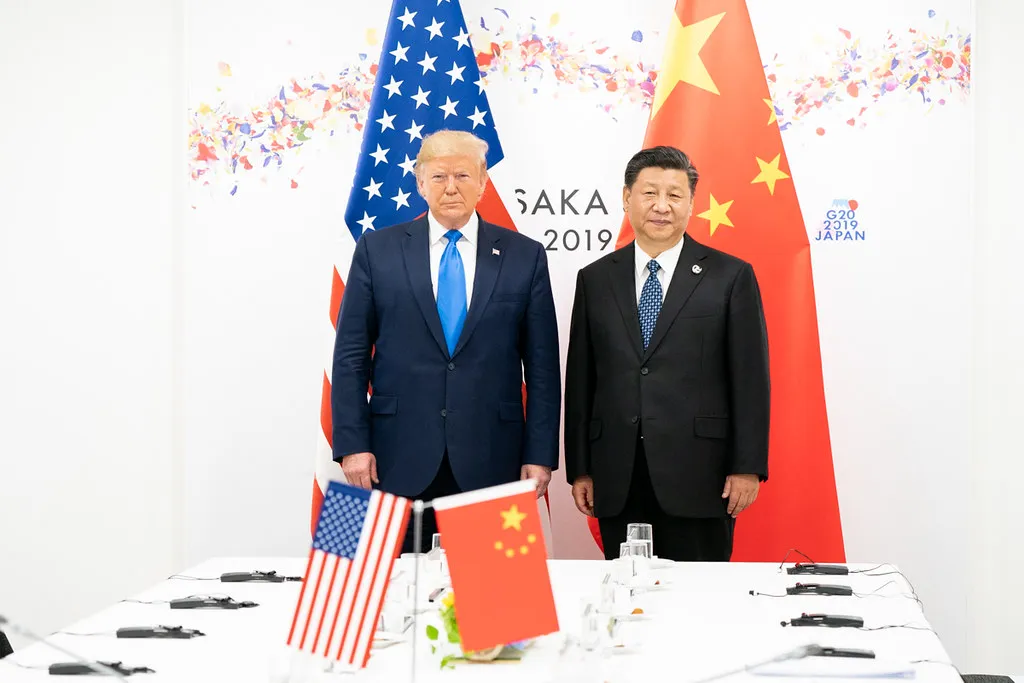
The Trump-Xi summit in Washington ended without a formal AI agreement, but a U.S. proposal for an AI incident line could matter more than the summit itself, according to analysts at the Institute for Security and Technology (IST). In a blog post, they argue the line will only work if both governments use it routinely, not just in emergencies.
- The Trump-Xi summit in Washington ended without a formal AI agreement, according to IST.
- Treasury Secretary Scott Bessent announced a U.S. proposal for an AI incident line after talks with Vice Premier He Lifeng.
- The U.S.-China AI dialogue is slated to meet next in Shenzhen in about two months.
- IST says the line should be built for routine use, modeled on the U.S.-Russia nuclear risk reduction centers.
- IST recommends separate tracks for loss of control and misuse.
A summit without an AI deal, but with a concrete proposal
Presidents Trump and Xi wrapped up their two-day summit in Washington without a formal AI deliverable, IST's Steven M. Kelly, Sylvia Mishra and Catherine Murphy write. Beijing's readout had Xi calling for the two sides to continue their AI dialogue and "jointly prevent the misuse and abuse of AI."
The most concrete step came earlier. After talks in New York with Vice Premier He Lifeng, Treasury Secretary Scott Bessent announced a U.S. proposal to open "an incident line so that we have constant communications." According to the authors, the two governments have also formalized a U.S.-China AI dialogue, which is slated to meet next in Shenzhen in about two months.
An early task will be agreeing on the leading AI dangers. Bessent described them as "uncontrollable agents" and non-state actors using AI to gain cyber and biological weapons capabilities. The incident line is a potential outcome of that process.
The authors note that neither leader wants an AI treaty. Trump has rejected any "globalist scheme" to control AI, and Xi resists outside constraints on China's own development. The dialogue asks neither side to slow down, only to agree on what is dangerous and to alert each other about AI-related security incidents.
Why a crisis hotline is not enough
Washington and Beijing already have a variety of military direct lines, including in the space and cyber domains. According to IST, what they lack is a track record of answering when it counts. After a U.S. Navy surveillance plane collided with a Chinese fighter jet in 2001, U.S. officials spent days trying to reach Chinese leaders. China also declined Pentagon calls after the 2023 balloon shootdown.
The authors say part of the problem is structural: in Beijing's system, answering a crisis call is a political decision, and picking up can look like rewarding the other side. Crisis lines work only when using them is already routine, they argue. The U.S.-Soviet link built that habit during the 1967 Six-Day War, the 1971 Indo-Pakistani War and the 1973 Yom Kippur War. The U.S.-China relationship never has.
The hardest design questions involve labs rather than governments. No one has settled how fast or by what method a frontier developer should report an incident to its own government, let alone how that report reaches the other side. Labs can often spot loss of control and misuse on systems they host, but for open-source models no lab sees how they are used, and detection falls to intelligence and law enforcement, if it happens at all. The authors also point to an asymmetry: U.S. labs are private companies reporting to a government, while Chinese labs operate in closer proximity to the state, and many of China's leading models are open-weight.
Four recommendations and two separate tracks
IST proposes four steps:
- Build the incident line for routine use. Model it on the U.S.-Russia National Nuclear Risk Reduction Centers, adopt shared definitions and thresholds first, and set rules for how quickly frontier AI developers notify their governments and what they disclose.
- Run parallel tracks on loss of control and misuse.
- Keep the dialogue off the bargaining table, so it meets on schedule even when relations fray.
- Accelerate the official track with bilateral working groups of engineers, researchers and national security practitioners that deliver draft definitions, reporting thresholds and stress-tested scenarios on a set timeline.
The authors separate the two risks because they raise different questions. Uncontrollable agents are a loss of control problem, where a system behaves in ways its operators did not intend. Cyber and biological threats from non-state actors are a misuse problem, where the system works as designed but gives a hacker or would-be bioterrorist capabilities they could not otherwise build. Misuse reporting will run into disputes over which hackers are truly non-state, while loss-of-control reporting will test how much labs are willing to disclose.
Is Beijing open to it?
Bessent has said China has surely had AI incidents but will not disclose them, and Xinhua's readout of the New York talks did not mention the incident line. The IST authors see more room for engagement. In their Track II engagements with Chinese counterparts, they report consistent willingness to work on AI crisis management, including incident reporting, communication channels and shared definitions. Interest was especially strong in IST's framework for monitoring AI loss of control, which adapts the intelligence community's indications and warning methodology to flag behaviors such as deception and self-preservation and grade incidents on a tiered severity schema.
Whether that openness carries over into official channels remains uncertain, the authors say. They argue industry belongs at the table because labs see incidents first, but should not set the agenda. For now, the test is whether the Shenzhen meeting and later sessions become a standing habit rather than a summit accessory.
Institute for Security and Technology: Before the first AI crisis, Washington and Beijing need a habit of talking