Armor CEO Tells GovWare: Govern AI Use, Don't Ban It
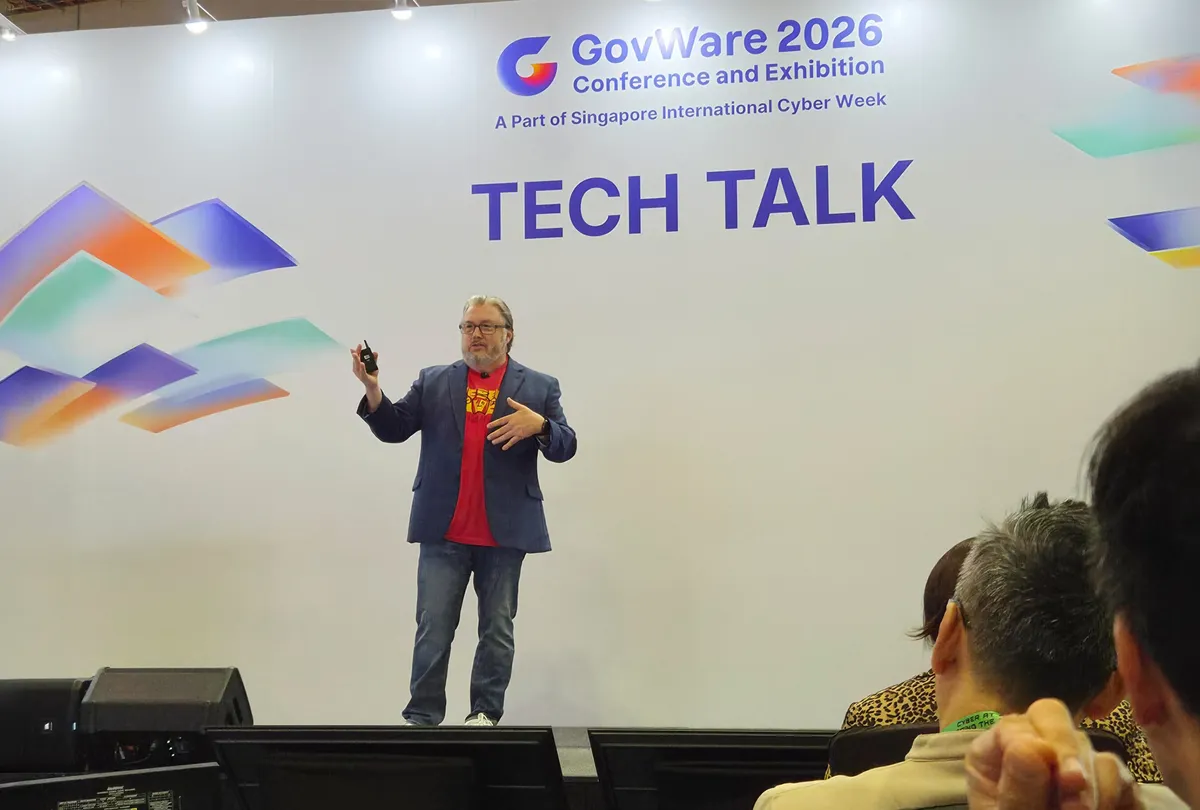
Banning AI does not work, Armor Founder and CEO Chris Drake told the GovWare 2026 conference in Singapore, arguing that CISOs should set the conditions for adoption and demand auditable evidence instead. In his Tech Talk Spotlights session, Drake said AI should complete useful business work automatically within policy.
- Armor CEO Chris Drake told GovWare 2026 in Singapore that banning AI does not work and CISOs should set conditions for adoption.
- Drake says agents can read files, send data and take actions, and that EDR alone cannot fully oversee local VMs.
- Protiviti's February 2026 AI Pulse Survey found 47% of large organizations had incomplete visibility into employees' AI tool use.
- Drake urged CISOs to secure a written mandate, named risk owners and an escalation path to the risk committee.
- Armor built Sovereign AI for its own operations and is demonstrating it at Booth A22 through October 15.
CISOs caught between speed and protection
Drake's session was titled "Once Again. AI Puts CISOs Between a Rock and a Hard Place." He said security leaders are under pressure to stay out of the way of AI innovation while keeping the business safe. Leaders see a competitive risk in moving too slowly, while CISOs must also protect customer trust, contractual commitments and operations.
According to Drake, AI is already arriving through employees and the tools they use, often without a separate security decision. He contrasted this with the move to the cloud, when security could assess a provider and influence which applications and data left the corporate environment. "With the cloud, the CISO at least got a say. With AI, nobody asked. Banning it doesn't work, and ignoring it is how the breach report gets written," he said.
Depending on permissions, an agent can read files, send data and take actions, Drake said. The risk can travel over an allowed connection even when the firewall works as configured.
Visibility gaps on employee machines and in supply chains
Drake pointed to gaps in visibility into local virtual machines. He said Anthropic documents that host endpoint detection and response (EDR) cannot inspect activity inside Cowork's local VM, while Docker documents that processes inside its local sandbox microVMs are invisible to the host. EDR alone cannot provide complete oversight, he said, and platform telemetry and network controls remain important.
He also noted that an employee clicking "Allow" does not settle whether the business approved the data access or processing. Suppliers add further exposure: a vendor that uses another AI provider to process an organization's data introduces fourth-party risk. Organizations need evidence of which providers are involved, where data is processed, what is retained and which contractual protections apply.
The release cites Protiviti's February 2026 AI Pulse Survey, which found that 47% of large organizations reported incomplete visibility into employees' use of AI tools. A useful, approved AI path can reduce the incentive to work around security, Drake said, though discovery and supplier oversight remain essential.
What Drake wants CISOs to do
Drawing on conversations across APAC, Drake described the pressure on CISOs who report to the CIO or CTO sponsoring an AI rollout. He urged them to lead the decision: agree on the business outcome, define what earns a yes and demand evidence that the controls and the business result work.
- A written mandate to approve, restrict or pause AI use.
- A named executive who owns each risk exception and its expiration date.
- An escalation path to the risk committee.
These are decisions about the conditions for adoption, not approval of every routine AI action, according to Drake.
He said data classification has moved from nice-to-have to must-have. Organizations must know what their data contains, who owns it and how it may be used. "AI cannot safely use data you cannot govern," he said. With that foundation, organizations should own the routing policy: use approved external models when data policy permits and private execution when required, then choose among permitted options based on task complexity, model capability, business needs and cost.
AI can then complete authorized work automatically, with records of the data accessed, policy decisions, models, routes, actions and outcomes. Those records let the organization reconstruct what happened without a person approving every step.
Armor's own platform and what it means for CISOs
Armor, a provider to regulated industries since 2009, said it faced the same challenge. Drake said the company was concerned about sending customer data through public AI services where controls and audit evidence could not meet its customer commitments. It built a governed AI platform for its own operations, now called Sovereign AI, and runs its business on it. Armor is demonstrating Sovereign AI at Booth A22 through October 15.
Drake closed with the principles behind the platform: know the data, preserve model choice, own routing policies, control actions and demand full auditability. He called for powerful agents and their credentials to run in governed, isolated, auditable environments with scoped access, rather than on employees' laptops. Before granting an AI tool access, he urged CISOs to ask three questions: What can it touch? Where can it send? Can we control what it does?
His message to CISOs was: "Yes. With rules. With authority. With evidence." The presentation is available at sovai.com/govware26. As the talk comes from a vendor that sells a product in this space, its recommendations reflect Armor's own approach.
PR Newswire: AI Needs a Governed Path, Not a Ban, Armor Founder Tells GovWare