Claude Code Settings Exposed 1,379 Secrets in Public GitHub Files
Claude Code’s approval settings exposed 1,379 distinct secrets across 1,122 public GitHub files, according to security company Apiiro’s research reported by The Hacker News. The findings show how a convenience setting can turn a developer’s command history into sensitive code committed to a repository.
- Apiiro found 1,122 public settings files containing at least one secret.
- The files held 1,379 distinct secrets, including 379 database passwords.
- Secret scanners missed 215 of the files in Apiiro’s test.
- Older Git versions and repository forks preserved additional secrets.
- The source recommends reviewing agent settings like application code.
One approval can save a password in plain text
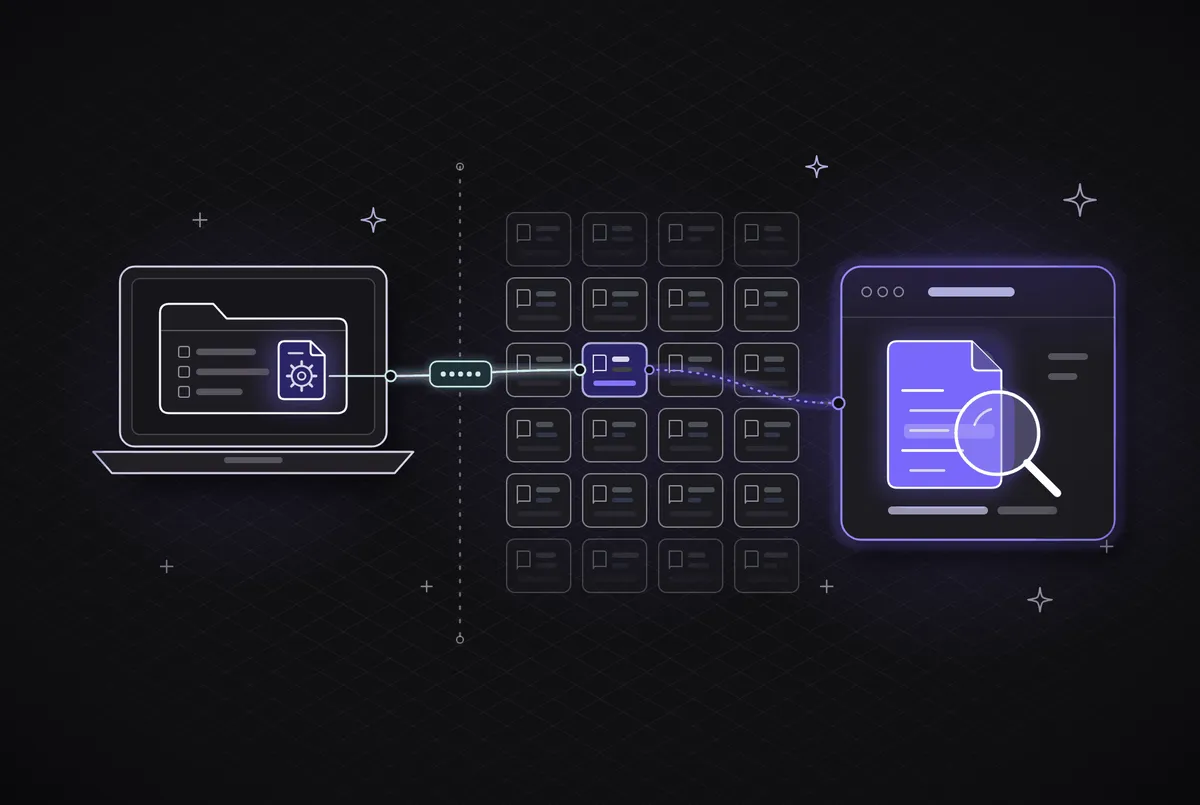
Claude Code asks before running most shell commands. When a developer selects “Yes, and don’t ask again,” the tool can save an allow rule in .claude/settings.local.json inside the project. The rule may be a pattern, such as npm test *, or a specific command.
When the command includes a password or token, the exact command can be stored in plain text, according to Apiiro’s research. Apiiro searched public GitHub between 1 and 3 Nov 2026 and published its research on 5 Nov 2026.
The researchers found 104,185 copies of .claude/settings.local.json across 103,617 repositories. Of those, 1,122 files in 1,105 repositories held at least one secret. The files contained 1,379 distinct secrets, including 379 database passwords, 43 SSH logins, 42 GitHub, GitLab and npm tokens, and 23 AWS keys.
Git history and scanners leave additional exposure
Apiiro did not test whether the credentials still worked, although one company it notified confirmed that its key had been live. The researchers also found 734 additional secrets in older versions across 509 repositories. In addition, 211 forks of 74 repositories carried the same secrets.
Removing a settings file does not remove earlier versions from Git history or copies in forks. Apiiro therefore advises rotating credentials before cleaning up the repositories.
Secret scanning also failed to catch every file in the test. Gitleaks flagged 564 of the 1,122 files, while TruffleHog flagged 643 when run without its verification step. Neither tool flagged 215 files. Passwords embedded in commands can resemble ordinary text rather than known key formats.
Anthropic said the file “is meant to stay local” and that Claude Code adds it to Git’s ignore list when it creates the file. Boris Cherny of the Claude Code team also wrote that it “is not a file you should check into source control” and said, “Regardless of what agent you use, you should have secret scanning enabled.”
Why agent settings need code review
The issue extends beyond one file. Agent folders such as .claude/, .cursor/, .gemini/ and .specstory/ can contain permissions, hooks, saved commands and other decisions that affect what an agent runs. The source argues these files should be treated like .env files and reviewed like application code.
In half of the repositories with a secret, the file had remained on the default branch for at least 217 days. Apiiro traced the files to 63 organizations, mostly software companies. In 539 of the 1,105 repositories, a commit listing Claude as a co-author changed the file.
Anthropic’s Cherny described the underlying problem as limited human attention. As agents ask developers to approve fewer commands, standing approvals can accumulate without anyone reviewing the complete settings file. The source recommends assigning ownership, checking agent settings on every pull request and using secret scanning. Qodo says its platform reviews pull requests, including changes to agent settings files, against repository and organization instructions, with findings that Claude Code can resolve through its plugin.