Factory Adds User Groups for Per-Person Enterprise Controls
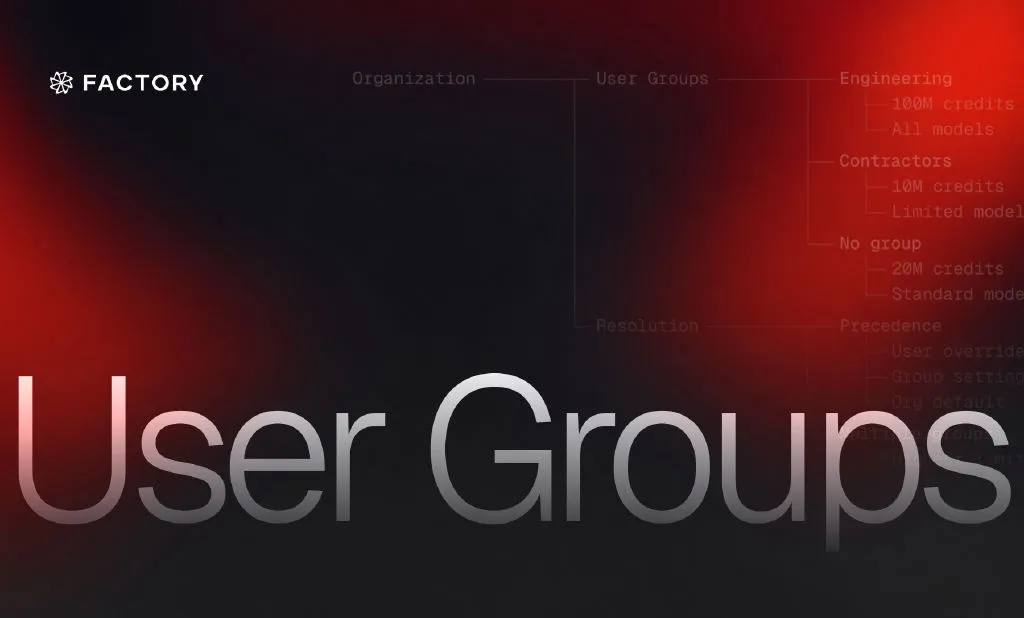
Factory has introduced User Groups, an extension to its Organization Model that lets enterprise customers apply usage limits and model access to selected people within and across organizations. The feature is available to enterprise customers with Directory Sync configured.
- User Groups applies usage limits and model access to selected people.
- Groups sync from an identity provider through Directory Sync.
- Individual overrides take priority over group and organization settings.
- The Organization API supports up to 100 groups per request.
- User Groups is available to enterprise customers with Directory Sync configured.
A layer of control within organizations
Factory announced the feature on November 6, 2026, following its introduction of the Factory Organization Model in August. Organizations give enterprises separate boundaries with their own members, admins, integrations, model access, data residency, and usage limits.
That structure did not cover cases where people inside the same organization needed different settings. Previously, administrators had to use per-user overrides or create separate organizations for different roles, which could require duplicating integrations and policies.
User Groups is designed for this situation. Groups are synchronized from an identity provider through Directory Sync. Administrators can configure settings such as a monthly usage limit or model access for a group, then select the organizations where those settings apply.
How settings are resolved
Factory applies settings according to a hierarchy. An individual override has priority, followed by the user's group settings in that organization, and then the organization's default. People who are not covered by a group use the organization's global settings.
For usage limits, a group limit can be higher or lower than the organization default. If a user belongs to several groups with limits, the highest limit applies. When no limit is set at any level, usage is unlimited.
Model access is resolved separately for each model. A group can allow a model excluded by the organization policy or block a model included by it. If a user belongs to several groups, a model is allowed when any of those groups allows it. Factory says settings are resolved on each request, so membership or configuration changes apply to a member's next request.
Administration and organization mapping
User Groups is managed in the Enterprise Admin Console, alongside organizations, billing, and identity. Enterprise owners can view groups synced through Directory Sync, configure their settings, and map them to organizations. The console lists each organization affected before a change is saved.
Group settings are configured per organization. The same group can therefore have a higher usage limit or broader model access in one organization, and no settings in another. Mapping a group does not change an organization's integrations, data residency, or administrators.
Configurations use the group's directory ID, so renaming a group in the identity provider does not affect its configuration. Administrators can inspect which level sets an individual user's limit, while managers can read and set group limits through the Organization API, with up to 100 groups per request. Changes made through the console or API are recorded in the audit log.
What the feature means for enterprise customers
Factory positions Organizations and User Groups as complementary controls. Organizations are intended for business units that need their own integrations, residency, or administrators. Groups are for people who share those boundaries but need different usage limits or model access.
Because groups come from the identity provider and are not tied to a single organization, existing groups can be mapped into a newly added organization rather than configured person by person. Changes to group membership apply in every organization where the group is mapped.
User Groups only affects settings on the User Groups page. Roles continue to come from the existing group-to-role mapping. Factory says the feature is available to enterprise customers with Directory Sync configured.
Factory: Extending the Factory Organization Model with User Groups