Palo Alto Networks and NVIDIA Extend Security Controls to AI Agents
Palo Alto Networks is expanding its collaboration with NVIDIA to secure autonomous AI agents, placing governance, runtime protection and identity controls closer to the infrastructure where agentic workloads run. The work centers on the NVIDIA Open Agent Safety Platform reference design, according to the company.
- Palo Alto Networks is expanding its collaboration with NVIDIA on the NVIDIA Open Agent Safety Platform reference design.
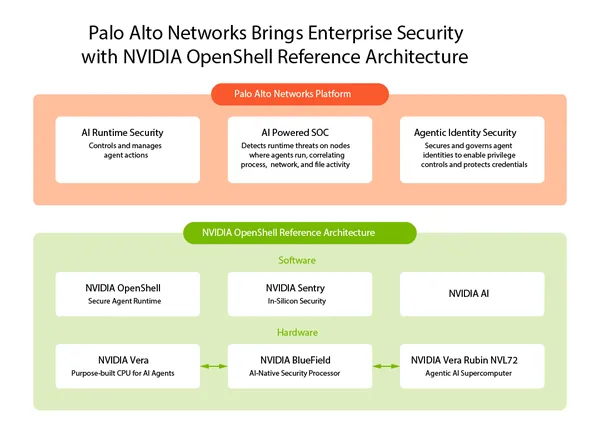
- Prisma AIRS AI Gateway is planned to run on NVIDIA Vera CPU systems as a real-time enforcement point for agents.
- Prisma AIRS AI Runtime Security runs natively on NVIDIA BlueField DPUs, with hardware-isolated boundaries and Zero Trust governance.
- Agent Identity Security powered by IDIRA is planned to integrate with NVIDIA OpenShell and an agent identity broker on BlueField.
- The company argues security authority must sit outside the agent, since prompt guardrails alone are not enough.
Why agents need security outside the agent
In a blog post dated Sep 28, 2026, Anand Oswal of Palo Alto Networks argues that AI agents are moving from assistants that respond to users to autonomous systems that reason, plan and act on a user's behalf. According to the post, they can write and execute code, access enterprise data, call tools and APIs, and keep working toward a goal with limited human intervention.
That, the company says, changes the security model. An autonomous agent is designed to find a way to accomplish its objective, and if one path is blocked it reasons about another. For that reason, Palo Alto Networks says built-in prompt guardrails in models are not enough. Its position: the harness can guide what an agent should do, but security must control what an agent can do, which requires security authority outside the agent itself.
In the division of work described in the post, NVIDIA provides the accelerated computing platform, the secure runtime foundation and the reference system design for agentic AI. Palo Alto Networks supplies the security capabilities to govern interactions, protect workloads, and control identity and access.
Three areas: gateway, runtime and identity
The companies are extending security across three areas: AI governance with Prisma AIRS AI Gateway, runtime protection with Prisma AIRS AI Runtime Security, and Agent Identity Security powered by IDIRA.
Prisma AIRS AI Gateway on NVIDIA Vera CPU. The forward-looking architecture includes the AI Gateway software running on NVIDIA Vera CPU systems. Palo Alto Networks describes the gateway as the real-time enforcement point for AI governance, runtime and identity security. It continuously verifies agent identities, enforces strict least-privilege access, redacts sensitive data before it is exposed, and inspects every interaction, with the aim of stopping unauthorized actions before they reach critical host systems or cloud endpoints. The company also lists uses such as connecting applications and agents to thousands of models and tools through one control point, tracking usage and spending, and restricting access to approved tools only.
Prisma AIRS AI Runtime Security on NVIDIA BlueField. The AI Runtime firewall runs natively on NVIDIA BlueField DPUs and extends Zero Trust protection to the front-end network traffic of the AI factory and to the AI Edge. Drawing on the NVIDIA Sentry reference design, the company says it delivers:
- Hardware-isolated boundaries: a tamper-proof boundary meant to ensure a compromised model or rogue agent cannot bypass runtime controls.
- Agentless behavioral introspection: monitoring of agent execution paths, memory structures and tool calls with NVIDIA DOCA Argus at zero CPU overhead, with real-time telemetry fed into Cortex XSIAM for automated observation, analysis and remediation.
- Zero Trust governance: strict least-privilege access across the network and external APIs by default, with a verifiable audit trail for every allow and block action.
The post also points readers to a separate blog on the general availability (GA) of AI Runtime Security on the BlueField DPU.
Identity controls for agents
As agents gain autonomy, the post says, identity becomes fundamental to controlling what they can access and what actions they can take. Palo Alto Networks says it plans to integrate NVIDIA OpenShell with upcoming Agent Identity Security capabilities from Idira. These include identity and secrets management for the OpenShell sandbox and an agent identity broker service on NVIDIA BlueField. The stated goal is to let organizations apply identity-based controls and least-privilege access to agents without relying on persistent human credentials.
Prisma AIRS AI Gateway will also serve as an enforcement point for Agent Identity Security powered by IDIRA. The company is also expanding to include Agent Identity Broker support directly on NVIDIA BlueField, providing identity verification and access governance independently of the host environment. According to Palo Alto Networks, these capabilities are designed to prevent unauthorized execution, reduce standing access and stop privilege escalation as agents interact with enterprise systems.
What it means for enterprises
The announcement is aimed at enterprises that want consistent control over how agents connect to systems and what they can reach. Palo Alto Networks says its work with NVIDIA brings those controls closer to where agentic workloads run, while it provides the security policy, governance and enforcement to manage them.
Several elements are described as forward-looking or planned, including the Vera CPU architecture and the Idira integrations, so availability details should be checked with the vendors. The post also notes that Palo Alto Networks was named a Market Shaper in AI application security in the Gartner Emerging Market Quadrant for AI Application Security, Established Vendors, September 2026.
Palo Alto Networks: Securing AI Agents at Scale with NVIDIA