LiteLLM
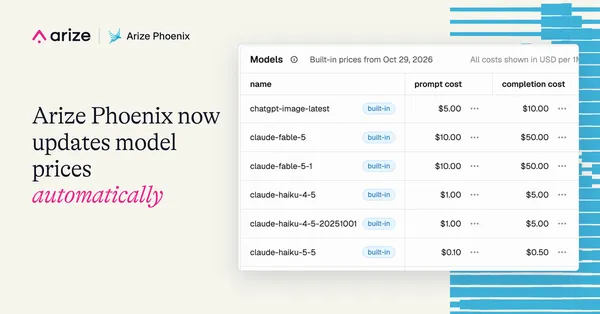
Arize Phoenix now updates LLM model prices automatically
Arize Phoenix, the open source agent observability tool, now updates its built-in model prices automatically, so servers no longer need a Phoenix upgrade to receive new…
JFrog Urges CISOs to Answer "Are We Exposed?" After Curl, PHP and LiteLLM Incidents
JFrog says recent vulnerabilities and a package compromise affecting Curl, PHP and LiteLLM show why security chiefs must be able to answer "Are we exposed?" quickly. In…
Fiddler AI: Patching Alone Cannot Contain the Risks of Enterprise AI Agents
Patching fixes software flaws, but it does not stop AI agents from leaking data, following malicious instructions or using stolen keys, according to a blog post from…
Malicious LiteLLM 1.107.0 on PyPI steals credentials, Wiz warns
Security firm Wiz reports that a malicious version of the LiteLLM Python package, 1.107.0, was uploaded to PyPI on October 21 and designed to steal credentials from…
Anaconda: Agentic AI Security Starts With Everything an Agent Loads
Anaconda argues that securing an AI agent means checking everything it loads, not only the model: skills, Model Context Protocol servers and Python packages included. In…
Check Point Finds Two High Risk Flaws in Popular LiteLLM AI Gateway
Check Point Research has discovered two high risk vulnerabilities in LiteLLM, the open source LLM gateway that organizations use to connect applications to AI providers…