Ultralytics adds HIPAA BAA for Enterprise Platform customers in medical imaging
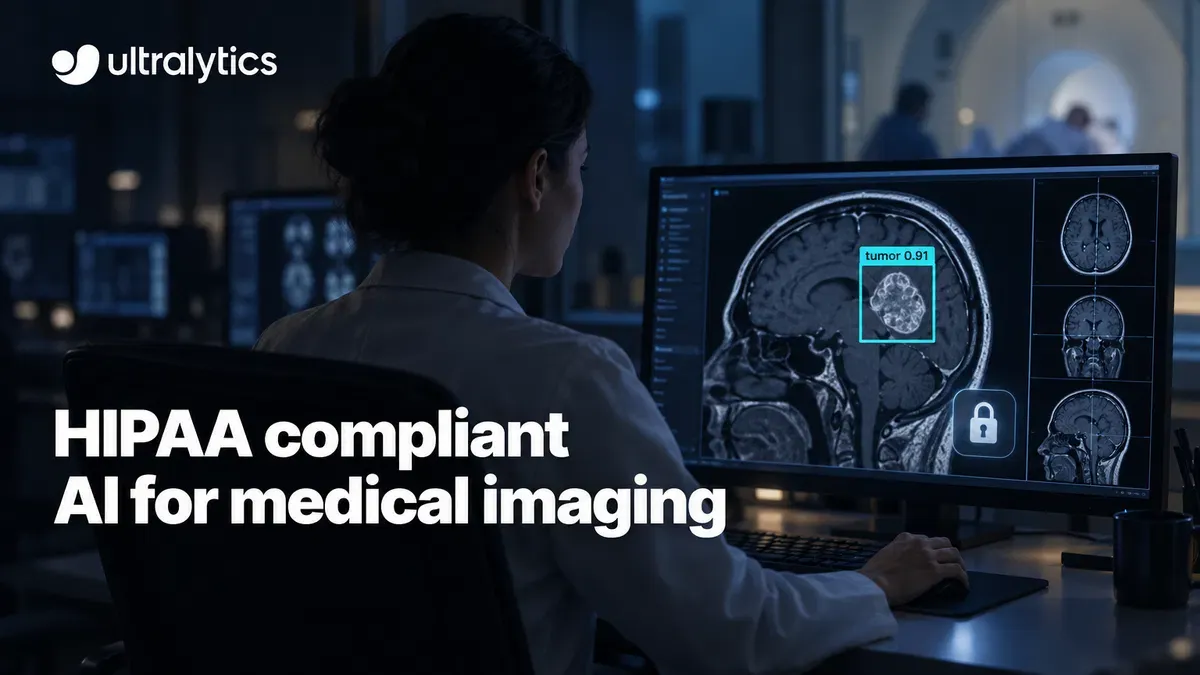
Ultralytics has completed a HIPAA Security Rule self-assessment covering Ultralytics Platform and Ultralytics YOLO, and Ultralytics Platform now offers a business associate agreement (BAA) to eligible Enterprise customers. According to the company, this changes what radiology, pathology and medical device teams can do with identifiable scans.
- Ultralytics Platform now offers a BAA to eligible Enterprise customers.
- Ultralytics completed a HIPAA Security Rule self-assessment based on NIST SP 800-66 Rev. 2, recorded as finished in October 2026.
- The self-assessment covers Ultralytics Platform and Ultralytics YOLO and is not an independent audit.
- PHI must not be uploaded without a BAA in effect; properly de-identified data can go to Platform on any plan.
- Customers choose a data region: US (Iowa), EU (Belgium) or AP (Taiwan).
What a BAA means in practice
Ultralytics stresses that HIPAA has no official certification. Quoting Google Cloud's HIPAA page, it notes that HHS "doesn't offer a certification program for HIPAA compliance". What a hospital security reviewer actually checks, the company says, is a signed BAA and a working security program.
The post draws on HHS guidance on HIPAA and cloud computing. According to that guidance, a covered entity may use a cloud service to store or process electronic protected health information (ePHI) only if it signs a HIPAA-compliant BAA with the provider. A provider that creates, receives, maintains or transmits ePHI is a business associate even if the data is encrypted and the provider holds no key. A BAA also does not authorize every use: the business associate may use PHI only as the contract permits, and training a model on patient records is a use the customer organization must assess itself.
For a medical imaging team, Ultralytics sums it up as three things: the vendor signs a BAA before any PHI arrives, the vendor runs a security program that meets the Security Rule, and the customer still handles access, de-identification and its own risk analysis.
What the self-assessment and the BAA cover
The self-assessment is based on NIST SP 800-66 Rev. 2 and covers Ultralytics Platform and Ultralytics YOLO. It builds on the company's ISO/IEC 27001:2022 certified information security management system and its SOC 2 report. The Ultralytics security team handbook records it as completed in October 2026. Ultralytics is clear that it is a self-assessment, not an independent audit.
The company lists other evidence on its Trust and Security page:
- ISO/IEC 27001:2022: verified by Insight Assurance in 2026, covering Ultralytics YOLO and Ultralytics Platform.
- SOC 2 Type I: also from Insight Assurance in 2026, with the full Platform in scope.
- Penetration test: an independent third party in 2026, covering Ultralytics Platform.
According to Ultralytics, controls that apply to every Platform plan include encryption at rest and in transit, enforced MFA, least-privilege IAM and annual penetration testing.
Section 3.5 of the Terms of Service sets the rules. Users must not upload PHI unless a BAA is in effect. Only Enterprise customers may be eligible, and no other plan can get one. The BAA takes effect only once both parties sign, and Ultralytics may limit it to specified services or configurations, so customers should confirm the exact scope while contracting. Customers decide whether they are a covered entity or business associate and own their HIPAA compliance, including any de-identification under 45 C.F.R. § 164.514. After signing, they remain responsible for classifying uploaded data, managing user access and securing team workstations.
De-identified scans and the training workflow
Not every medical image is PHI. Ultralytics says properly de-identified datasets can go to Platform on any plan. It points to the two HHS methods: Safe Harbor, which removes the 18 identifier types listed in 45 C.F.R. § 164.514(b)(2), and Expert Determination, where a qualified expert documents that re-identification risk is very small. Imaging brings its own traps: DICOM headers carry patient identifiers, full-face photographs are one of the 18 identifiers, and text burned into pixels needs checking as well as metadata. A dataset that meets neither method should be treated as PHI.
For work under a signed BAA, the post advises preparing PNG or TIFF images locally, checking metadata and burned-in identifiers, and inspecting converted images before upload. Converting DICOM does not de-identify on its own.
Workspace setup matters before the first upload. Customers choose a data region during onboarding: US (Iowa), EU (Belgium) or AP (Taiwan). According to the Platform documentation, datasets, models and managed training data stay in that region, and a later move needs a support request. Account-level data such as profile and billing records is processed globally. Enterprise visibility defaults to Private, but Ultralytics advises verifying that each dataset and project is Private before uploading PHI. Four team roles (Owner, Admin, Editor, Viewer) support least privilege, and clinicians who correct and save labels need Editor or higher. SSO/SAML lets access follow the customer's identity provider.
What it means for medical imaging teams
For teams that want to annotate, train and deploy on identifiable scans, the news opens a contractual route on Ultralytics Platform, but only for eligible Enterprise customers and only within the services and configurations the executed BAA covers. Teams using other plans can still work with properly de-identified data. The post also compares this route with keeping all data in-house on self-hosted Ultralytics YOLO, though the provided text does not detail that comparison.